Risk Score Explained
Every finding, asset, and assessment score in Risk Assessment comes out of a defined formula. This page explains what that formula is, how to see why a given finding got the score it did, and what happens when you change your organization's criteria.
1. The formula is a registered, versioned definition
The scoring formula isn't a constant hidden in the code — it's a versioned definition you can view directly in the settings screen. The version in effect now is finding-v1.
finding-v1 produces the same numbers as beforefinding-v1 produces exactly the same scores as the formula it replaces (finding-v0), which used to exist only as hardcoded constants. What changed isn't the arithmetic — it's three things: every finding now carries its basis, the bins and mappings are read from your organization's criteria, and a CVSS base score is shown alongside for reference. If you haven't changed any criteria, your scores are exactly what they used to be.
Assessments completed before this change show as finding-v0 — the formula that actually produced their scores. Every new assessment uses finding-v1.
2. How one finding's score is calculated
- Likelihood — the average EPSS (exploit prediction score) across the vulnerabilities linked to the finding falls into one of several bins.
- Impact — the finding's severity is mapped to an impact level.
- Likelihood and impact are looked up in a matrix to produce the final risk level (Very High/High/Moderate/Low/Very Low).
The bin boundaries and the severity-to-impact mapping are read from your organization's risk criteria (section 4 below). If you haven't changed anything, these are this product's defaults.
The finding's detail view shows the basis needed to reproduce this calculation:
- the average EPSS value, which bin it fell into, and whether that bin boundary is the default or one your organization set
- the severity and the impact it was mapped to
- the exact cell of the matrix the score landed on
- whether the finding touches a vulnerability with confirmed real-world exploitation (CISA KEV) — a display and sorting signal only, not an input to the score
- the formula version and criteria version that produced this score
An explanation sentence built from this basis is shown right on the finding. That sentence is never stored — it's generated fresh from the basis every time you look, so a later change to how the basis is worded can never leave a stored sentence saying something the underlying basis no longer supports.
3. CVSS is shown for reference only
When a CVSS base-score feed is configured, the highest base score among the finding's linked vulnerabilities is shown alongside the basis. When it isn't configured, the basis reads "no CVSS feed configured" — never a score of 0, because that would misleadingly read as "low," not "absent."
CVSS never enters the risk level or score calculation, in either case. It's shown next to the likelihood/impact calculation purely as an additional signal to consider.
4. Your organization's risk criteria
The criteria live on the Settings screen in the console's top menu. This screen gathers the settings that apply to every connection in your organization, and has two tabs.
- Risk Criteria – the risk criteria described below, and the list of registered scoring formulas (Scoring formulas)
- Organization – a note that company profile, members and subscription are managed in the organization portal, with an Open the portal link (see Organization Portal)
The criteria on the Risk Criteria tab can be read by anyone in the organization and changed only by an admin. For non-admins they are shown read-only with the note These can be read by anyone in the organization and changed by an administrator. If your subscription plan does not include risk criteria settings, a notice saying so replaces the form, and the values and formulas currently in effect remain fully visible.
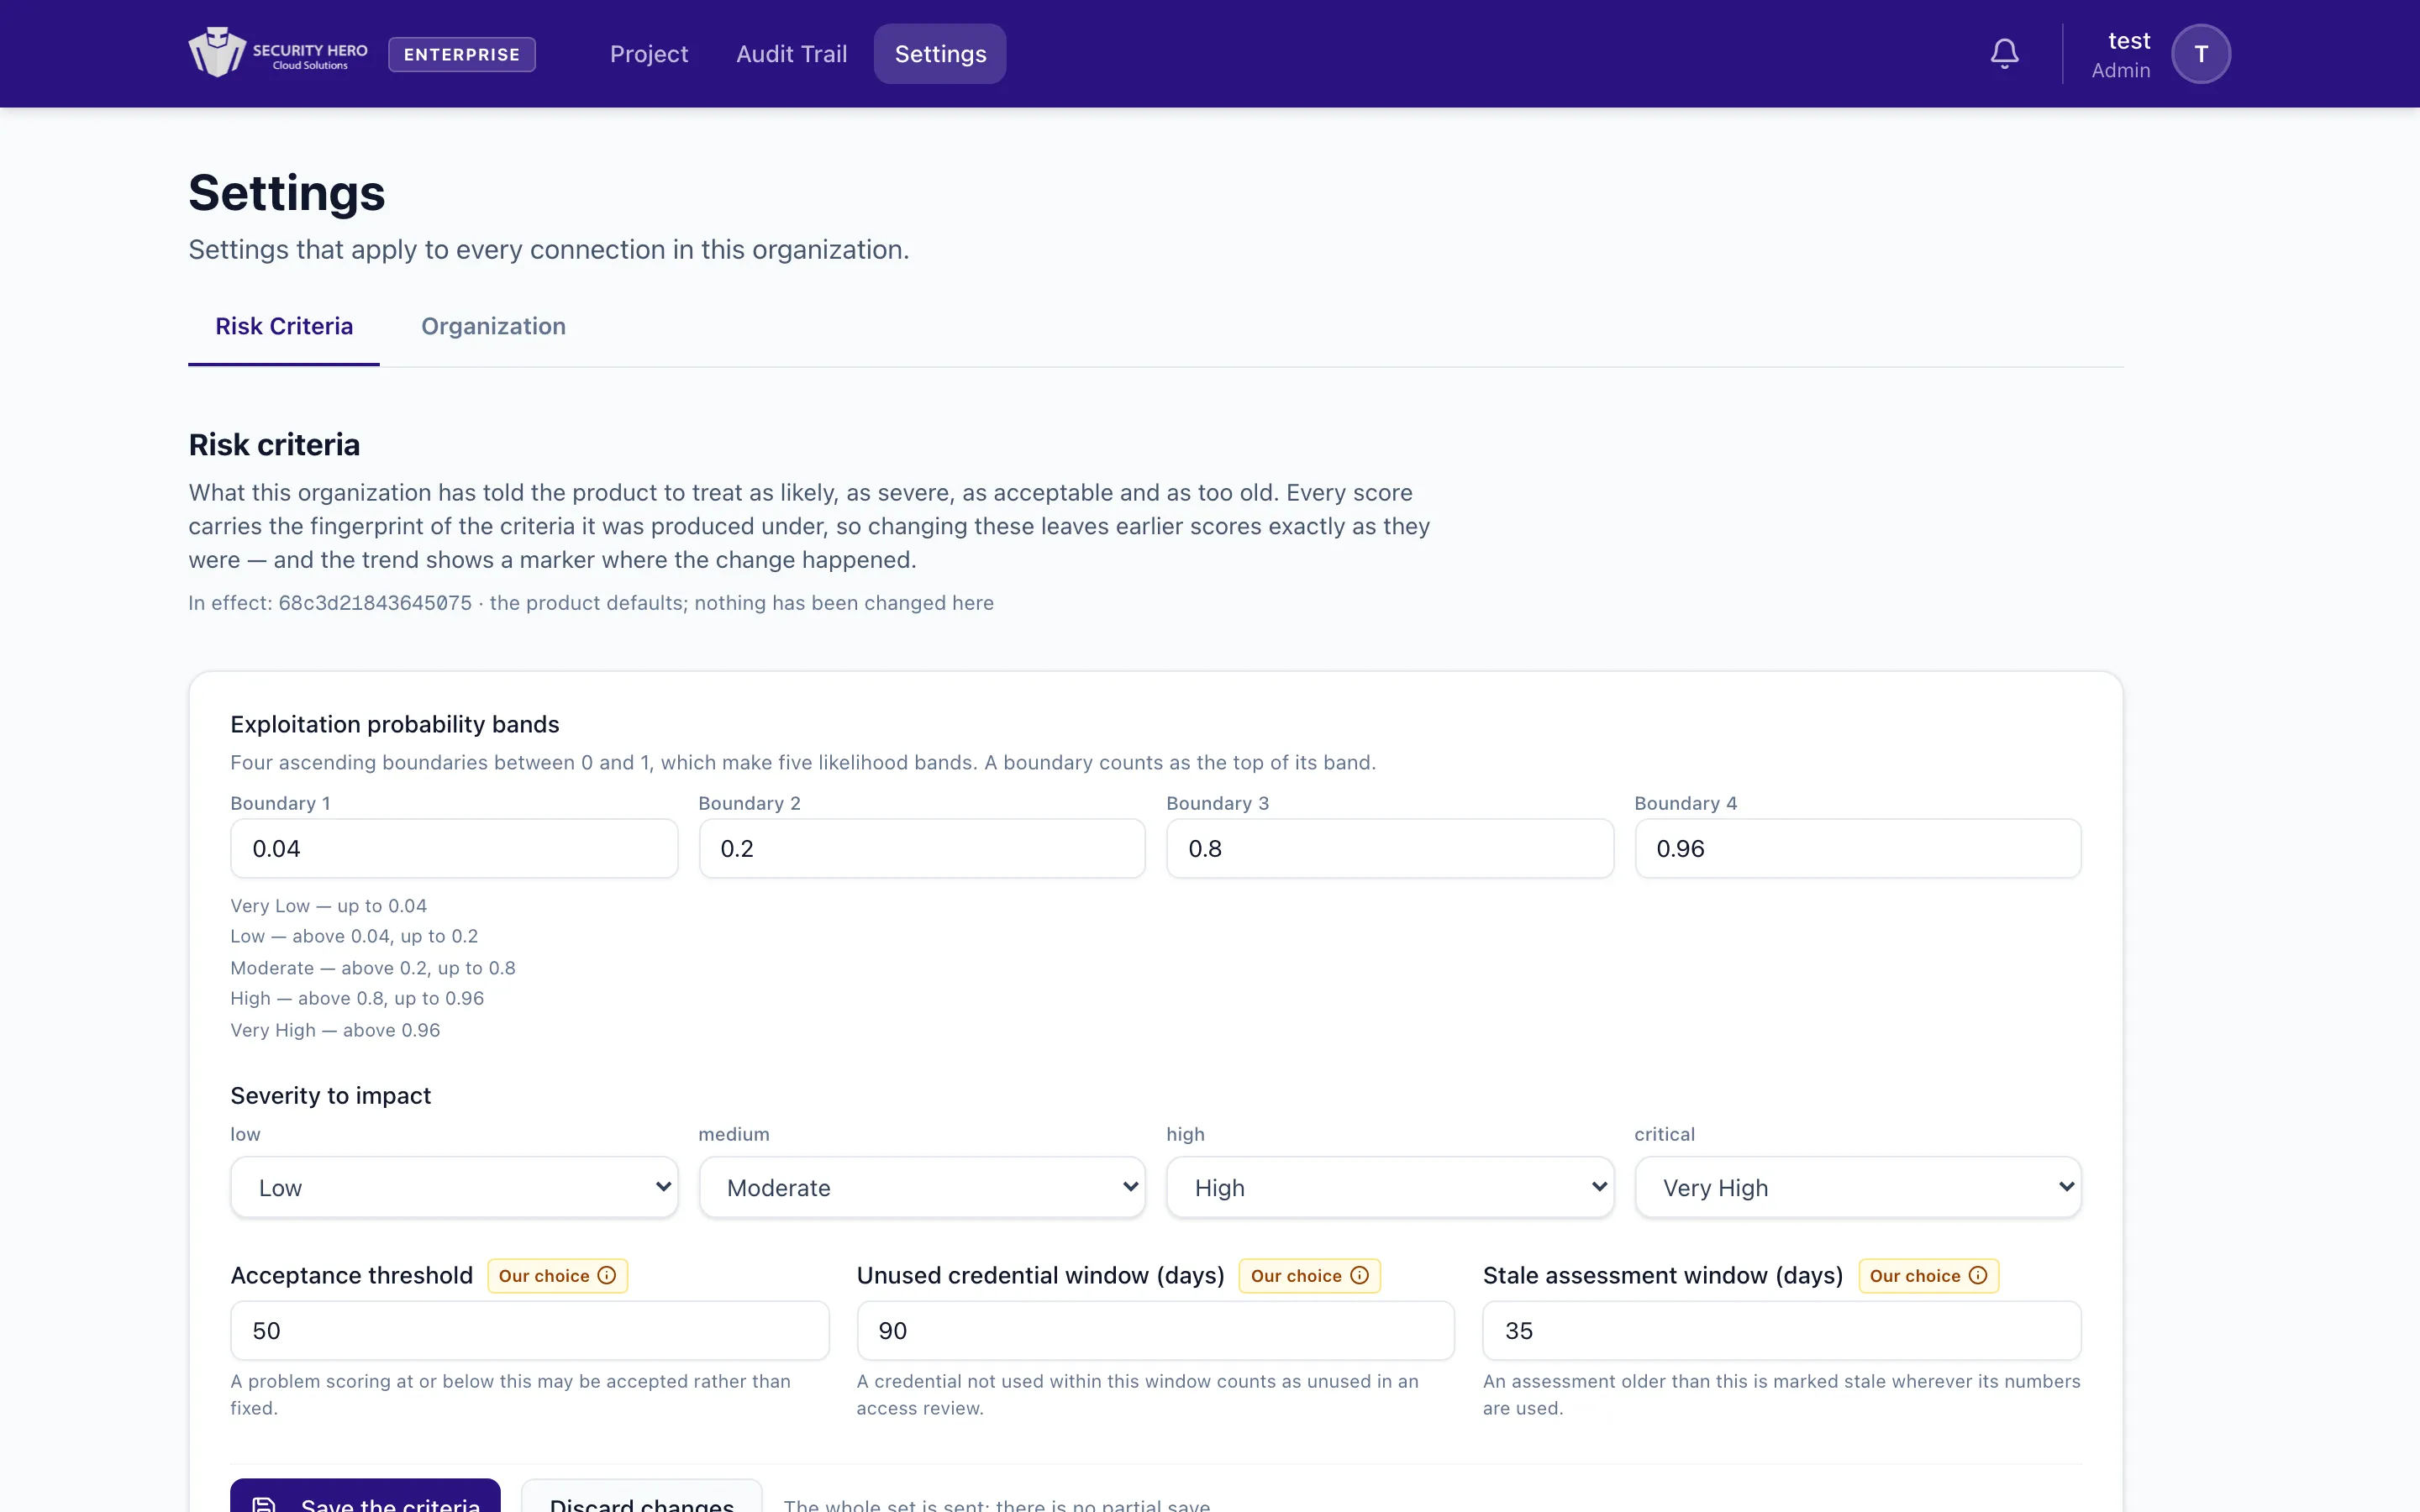
The In effect: line at the top of the tab shows the criteria version currently in effect, and whether the values were set by your organization (chosen here, with the last change date and who made it) or are the product defaults (the product defaults; nothing has been changed here). The editable fields are:
- Exploitation probability bands – EPSS bin boundaries (four values, ascending)
- Severity to impact – severity-to-impact mapping
- Acceptance threshold – the threshold for accepting (excepting) a problem. A problem scoring at or below this may be accepted rather than fixed.
- Unused credential window (days) – how many days without use before a credential counts as "unused" in an Access Review
- Stale assessment window (days) – an assessment older than this is marked stale wherever its numbers are used.
Clicking Save the criteria saves the whole set at once (there is no partial save). Discard changes reverts unsaved edits.
The Scoring formulas section at the bottom of the tab lists every registered formula, and each assessment records which formula scored it (see 1. The formula is a registered, versioned definition).
Fields that aren't set by any regulation — they're a choice this product made, not a requirement any framework imposes — carry a distinct badge on screen. The 90-day unused-credential default, for instance, isn't a requirement of any framework; it's this product's own default. When an auditor asks where a number like that came from, both the finding basis and every report distinguish "this is a regulatory requirement" from "this is a value the product chose."
Changing a criteria value changes its fingerprint (the criteria version), and the new criteria apply starting with the next assessment. Scores already recorded do not change — every assessment stores the criteria version that was in effect when it ran.
5. Asset and assessment scores
When an asset has more than one finding, its risk level is the highest (worst) among them. An assessment's overall score is the average of every finding score in that assessment.
6. Trend and formula breaks
The Assessment History chart plots score over time. Whenever the formula version, criteria version, or scanner version changes between two consecutive assessments, that point is marked as a break.

If the scanner was upgraded (adding checks) or your organization changed its criteria in between, the two scores on either side of a break weren't measured with the same yardstick. A line drawn straight through without marking that would wrongly suggest things got better or worse.
7. Related pages
This is the same formula used by Controls' automated indicator and by Risk Assessment results. To hand this score, along with its basis, to an auditor as part of a signed bundle, see Evidence Package.