Data Security
Security Hero RMF can store sensitive data, such as raw scan results, in your own AWS account, encrypted with a key you control.
This page explains the data sovereignty model and how to connect an encryption key (BYOK) and data storage (your S3).
1. Data sovereignty model
Security Hero RMF handles data in two streams.
- Raw (sensitive) data – scan result details, original asset properties, IAM policy documents, permission risk analysis results and so on. Once you connect an S3 bucket, this data is stored in your own S3, encrypted with SSE-KMS (your CMK).
- Metadata for display + references (pointers) – the minimum summary information needed for lists, aggregates and on-screen display, plus a reference to the S3 location of the raw data. This is kept in the service database and isolated per tenant (organization).
In other words, the most sensitive data stays inside your AWS boundary, and if you disable the key, the service can no longer decrypt that data.
 Security Hero RMF


Connecting an encryption key (BYOK) and data storage (S3) is optional. Every feature works without them; in that case, raw data is kept securely in storage managed by the service. You can connect them at any time to move where the data is kept into your own account.
2. Prerequisites
Both features are set up in Project Settings > AWS Connection, and appear on screen only after the AWS account connection is complete.
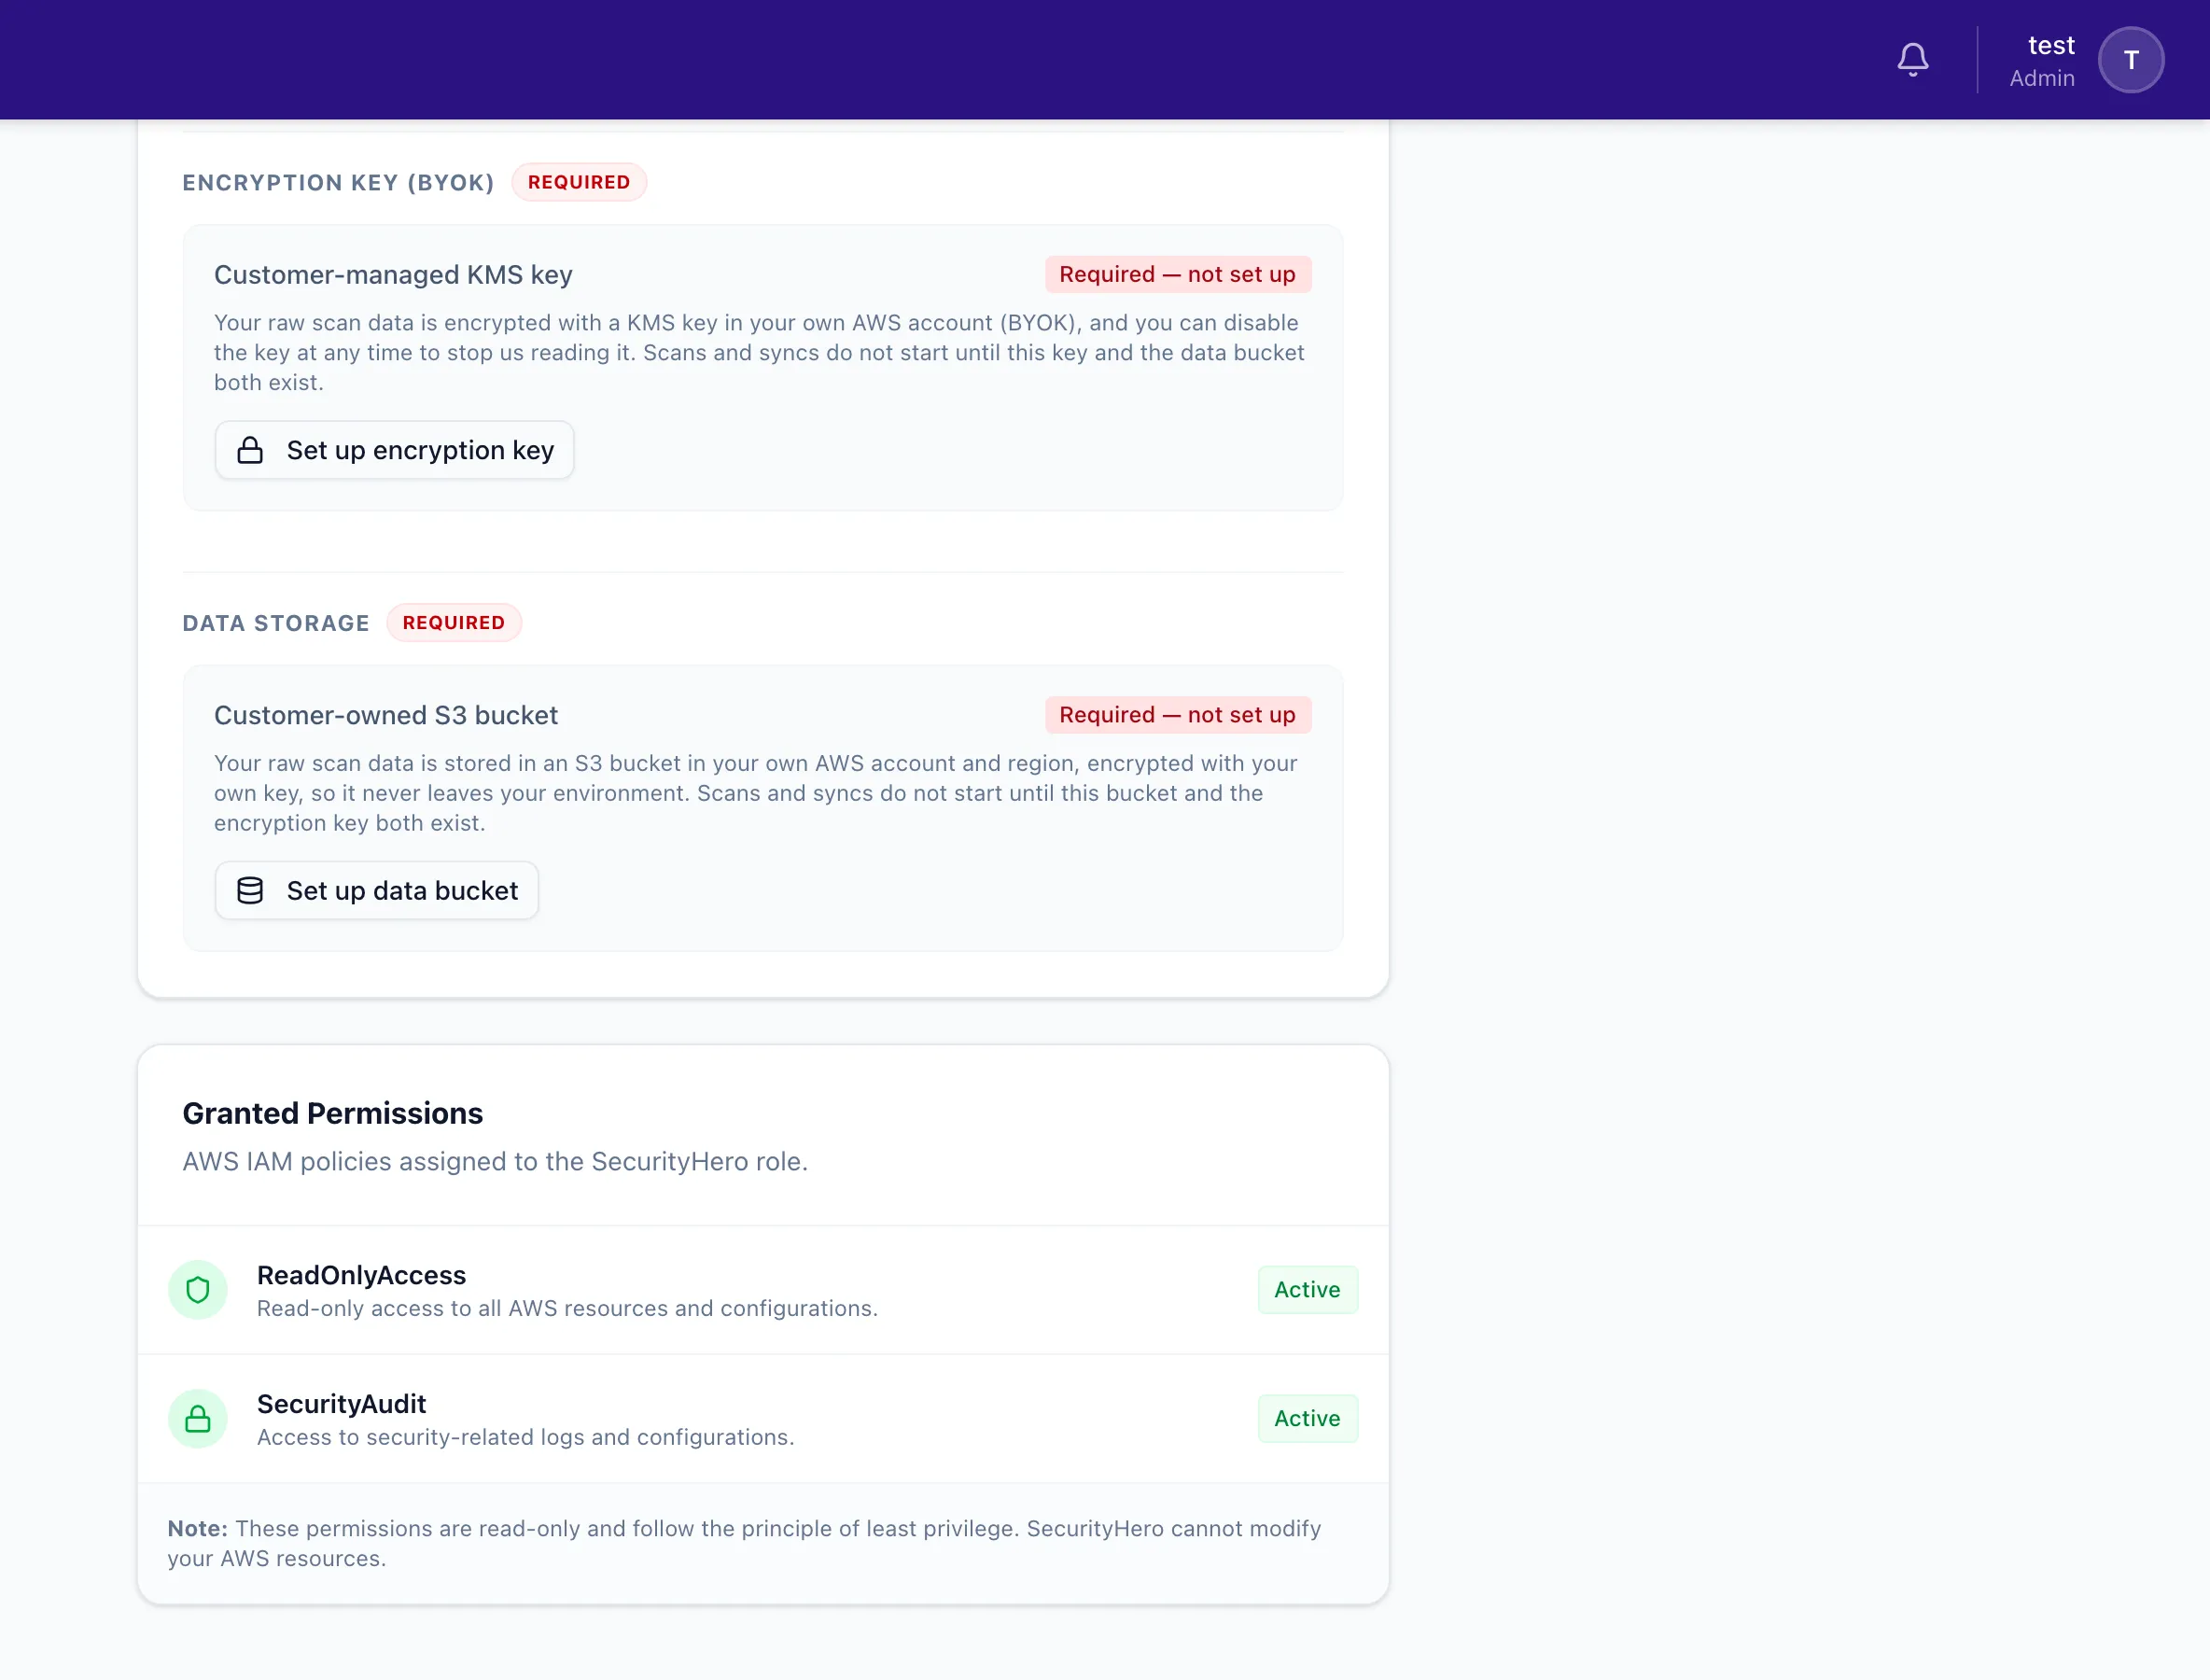
- For connecting AWS, see Project Settings.
- Resources are created with CloudFormation, so you need permission to create stacks in the target AWS account.
- Recommended order: ① encryption key (BYOK) → ② data storage (S3). The S3 bucket encrypts data with this key, so it is best to prepare the key first.
3. Connecting an encryption key (BYOK)
Location: Project Settings > AWS Connection > Encryption Key (BYOK)
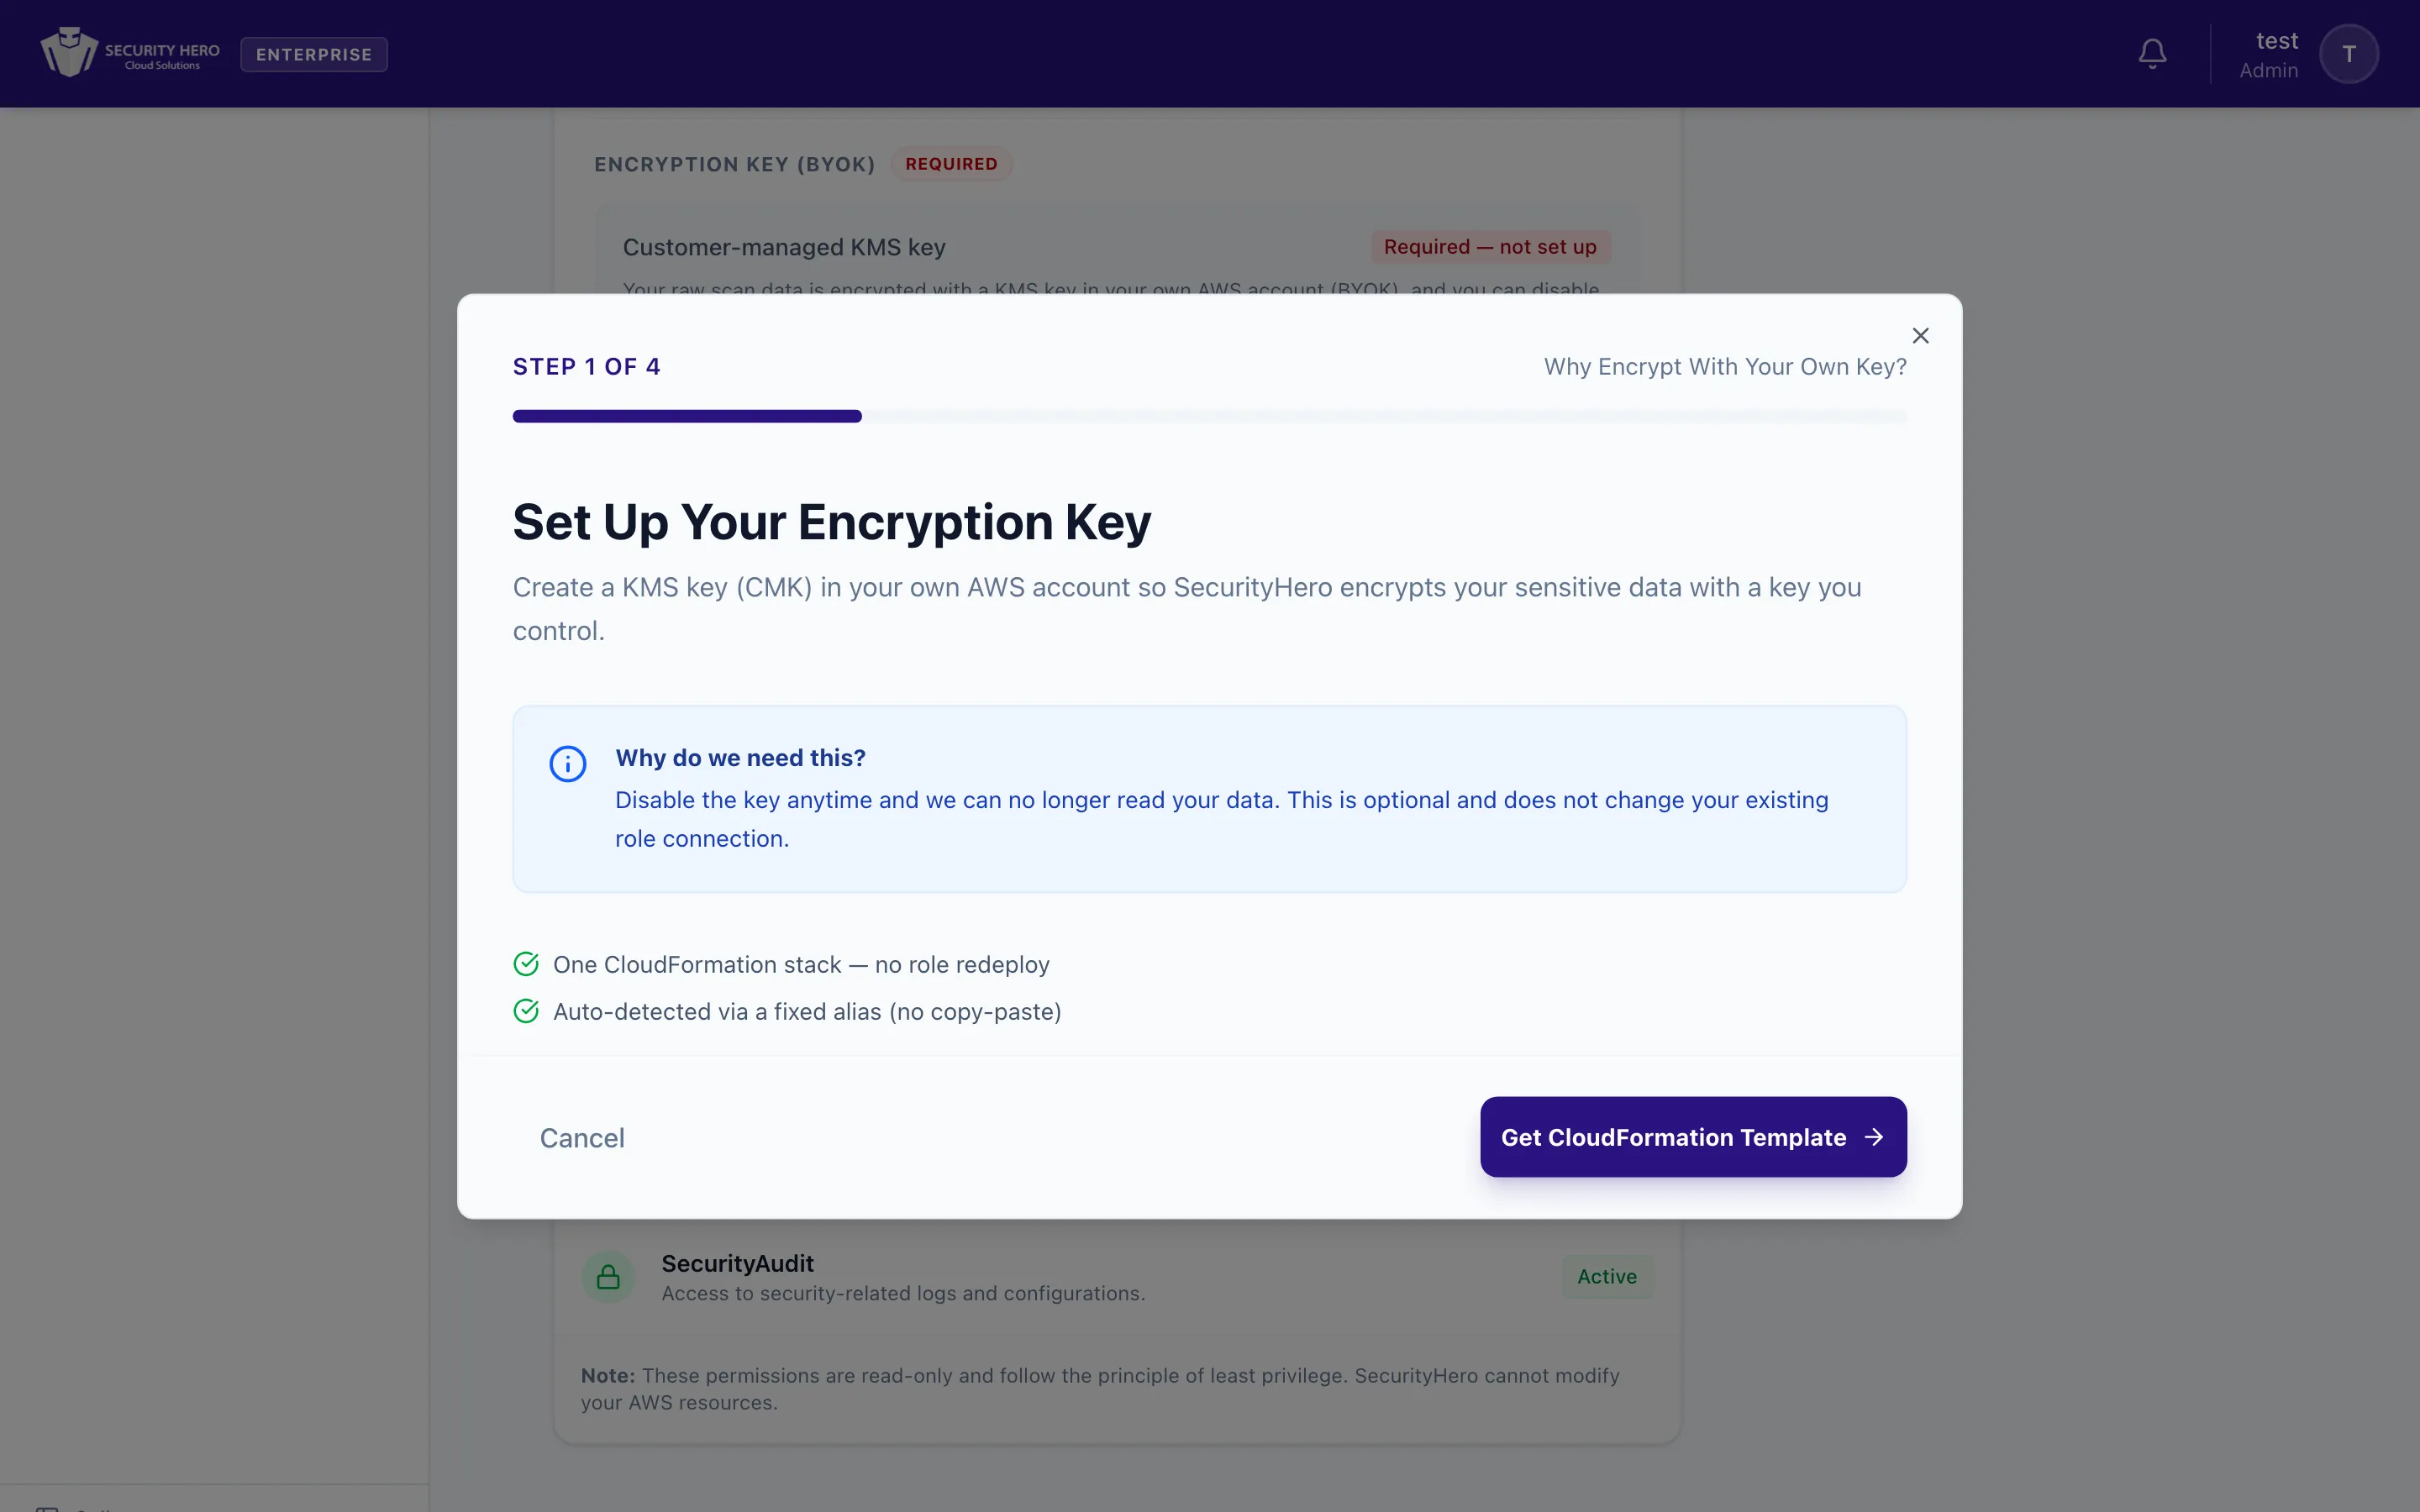
Create a KMS key (CMK) in your AWS account so that Security Hero encrypts sensitive data with a key you control. This does not change the existing role connection, and the role does not need to be redeployed.
- Start setup: Click Set up encryption key in the section. (The status badge shows
Not set upbefore setup andConnectedwhen done.) - Get the template: Review the guidance and click Get CloudFormation template.
- Download the template and create the stack:
- Download the template (
securityhero-kms.yaml) with Download CloudFormation Template. - In the AWS CloudFormation console, create a stack with Create stack → upload the downloaded template.
- Wait until the stack status becomes CREATE_COMPLETE.
- Download the template (
- Connect and verify: Return to the screen and click Verify & Connect. The key is detected automatically by the fixed alias
alias/securityhero, so you do not need to copy and paste the ARN. - Done: The message
Encryption key connectedis shown together with the connected key ARN.
After connecting, the section shows the key ARN and region, and you can verify again at any time with Re-verify.
If you disable the key, Security Hero can no longer read data encrypted with it. Control over the data always stays with you.
4. Connecting data storage (customer-owned S3)
Location: Project Settings > AWS Connection > Data Storage
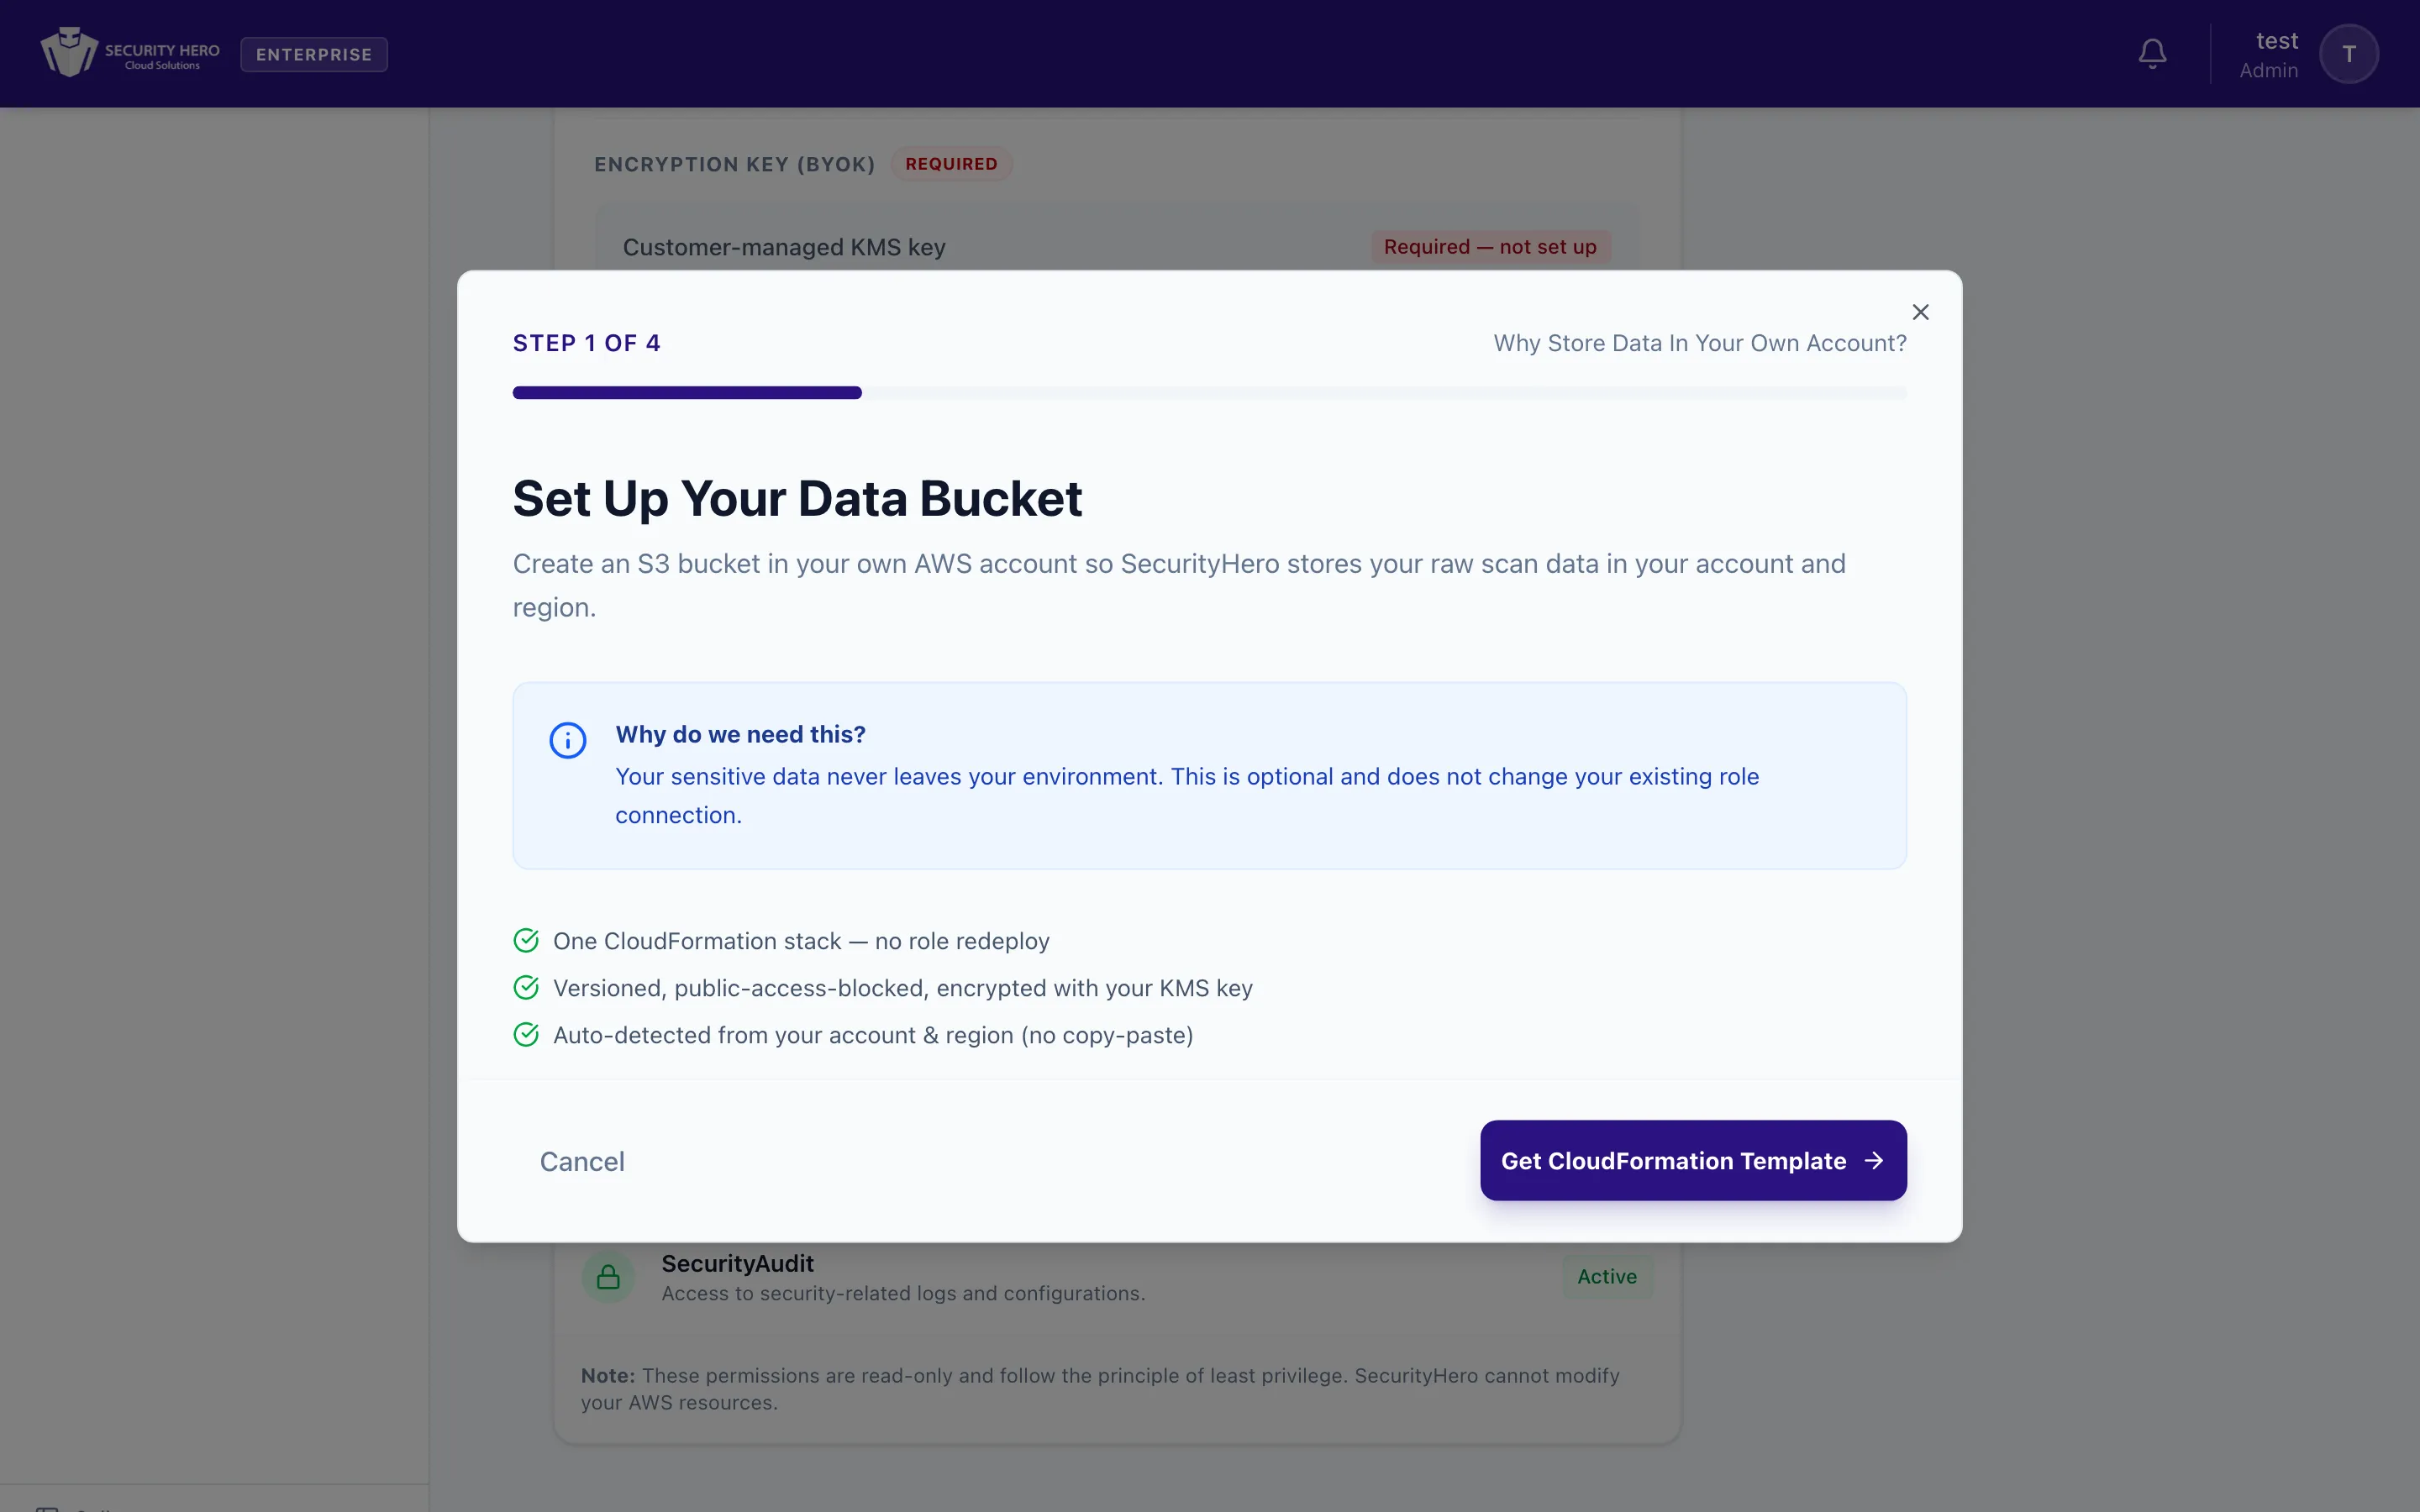
Create an S3 bucket in your AWS account to keep raw scan result data in your account and region. The bucket has versioning and public access blocking applied, and the data is encrypted with your KMS key.
- Start setup: Click Set up data bucket in the section.
- Get the template: Click Get CloudFormation template.
- Download the template and create the stack:
- Download the template (
securityhero-data-bucket.yaml) with Download CloudFormation Template. - Create the stack in the CloudFormation console and wait for CREATE_COMPLETE.
- Download the template (
- Connect and verify: Click Verify & Connect. The bucket is detected automatically from the account and region.
- Done: The message
Data bucket connectedis shown together with the bucket name and region.
Data storage encrypts the raw data with the encryption key (BYOK) above. For the best protection, we recommend completing 3. Connecting an encryption key first.
5. Checking the connection status
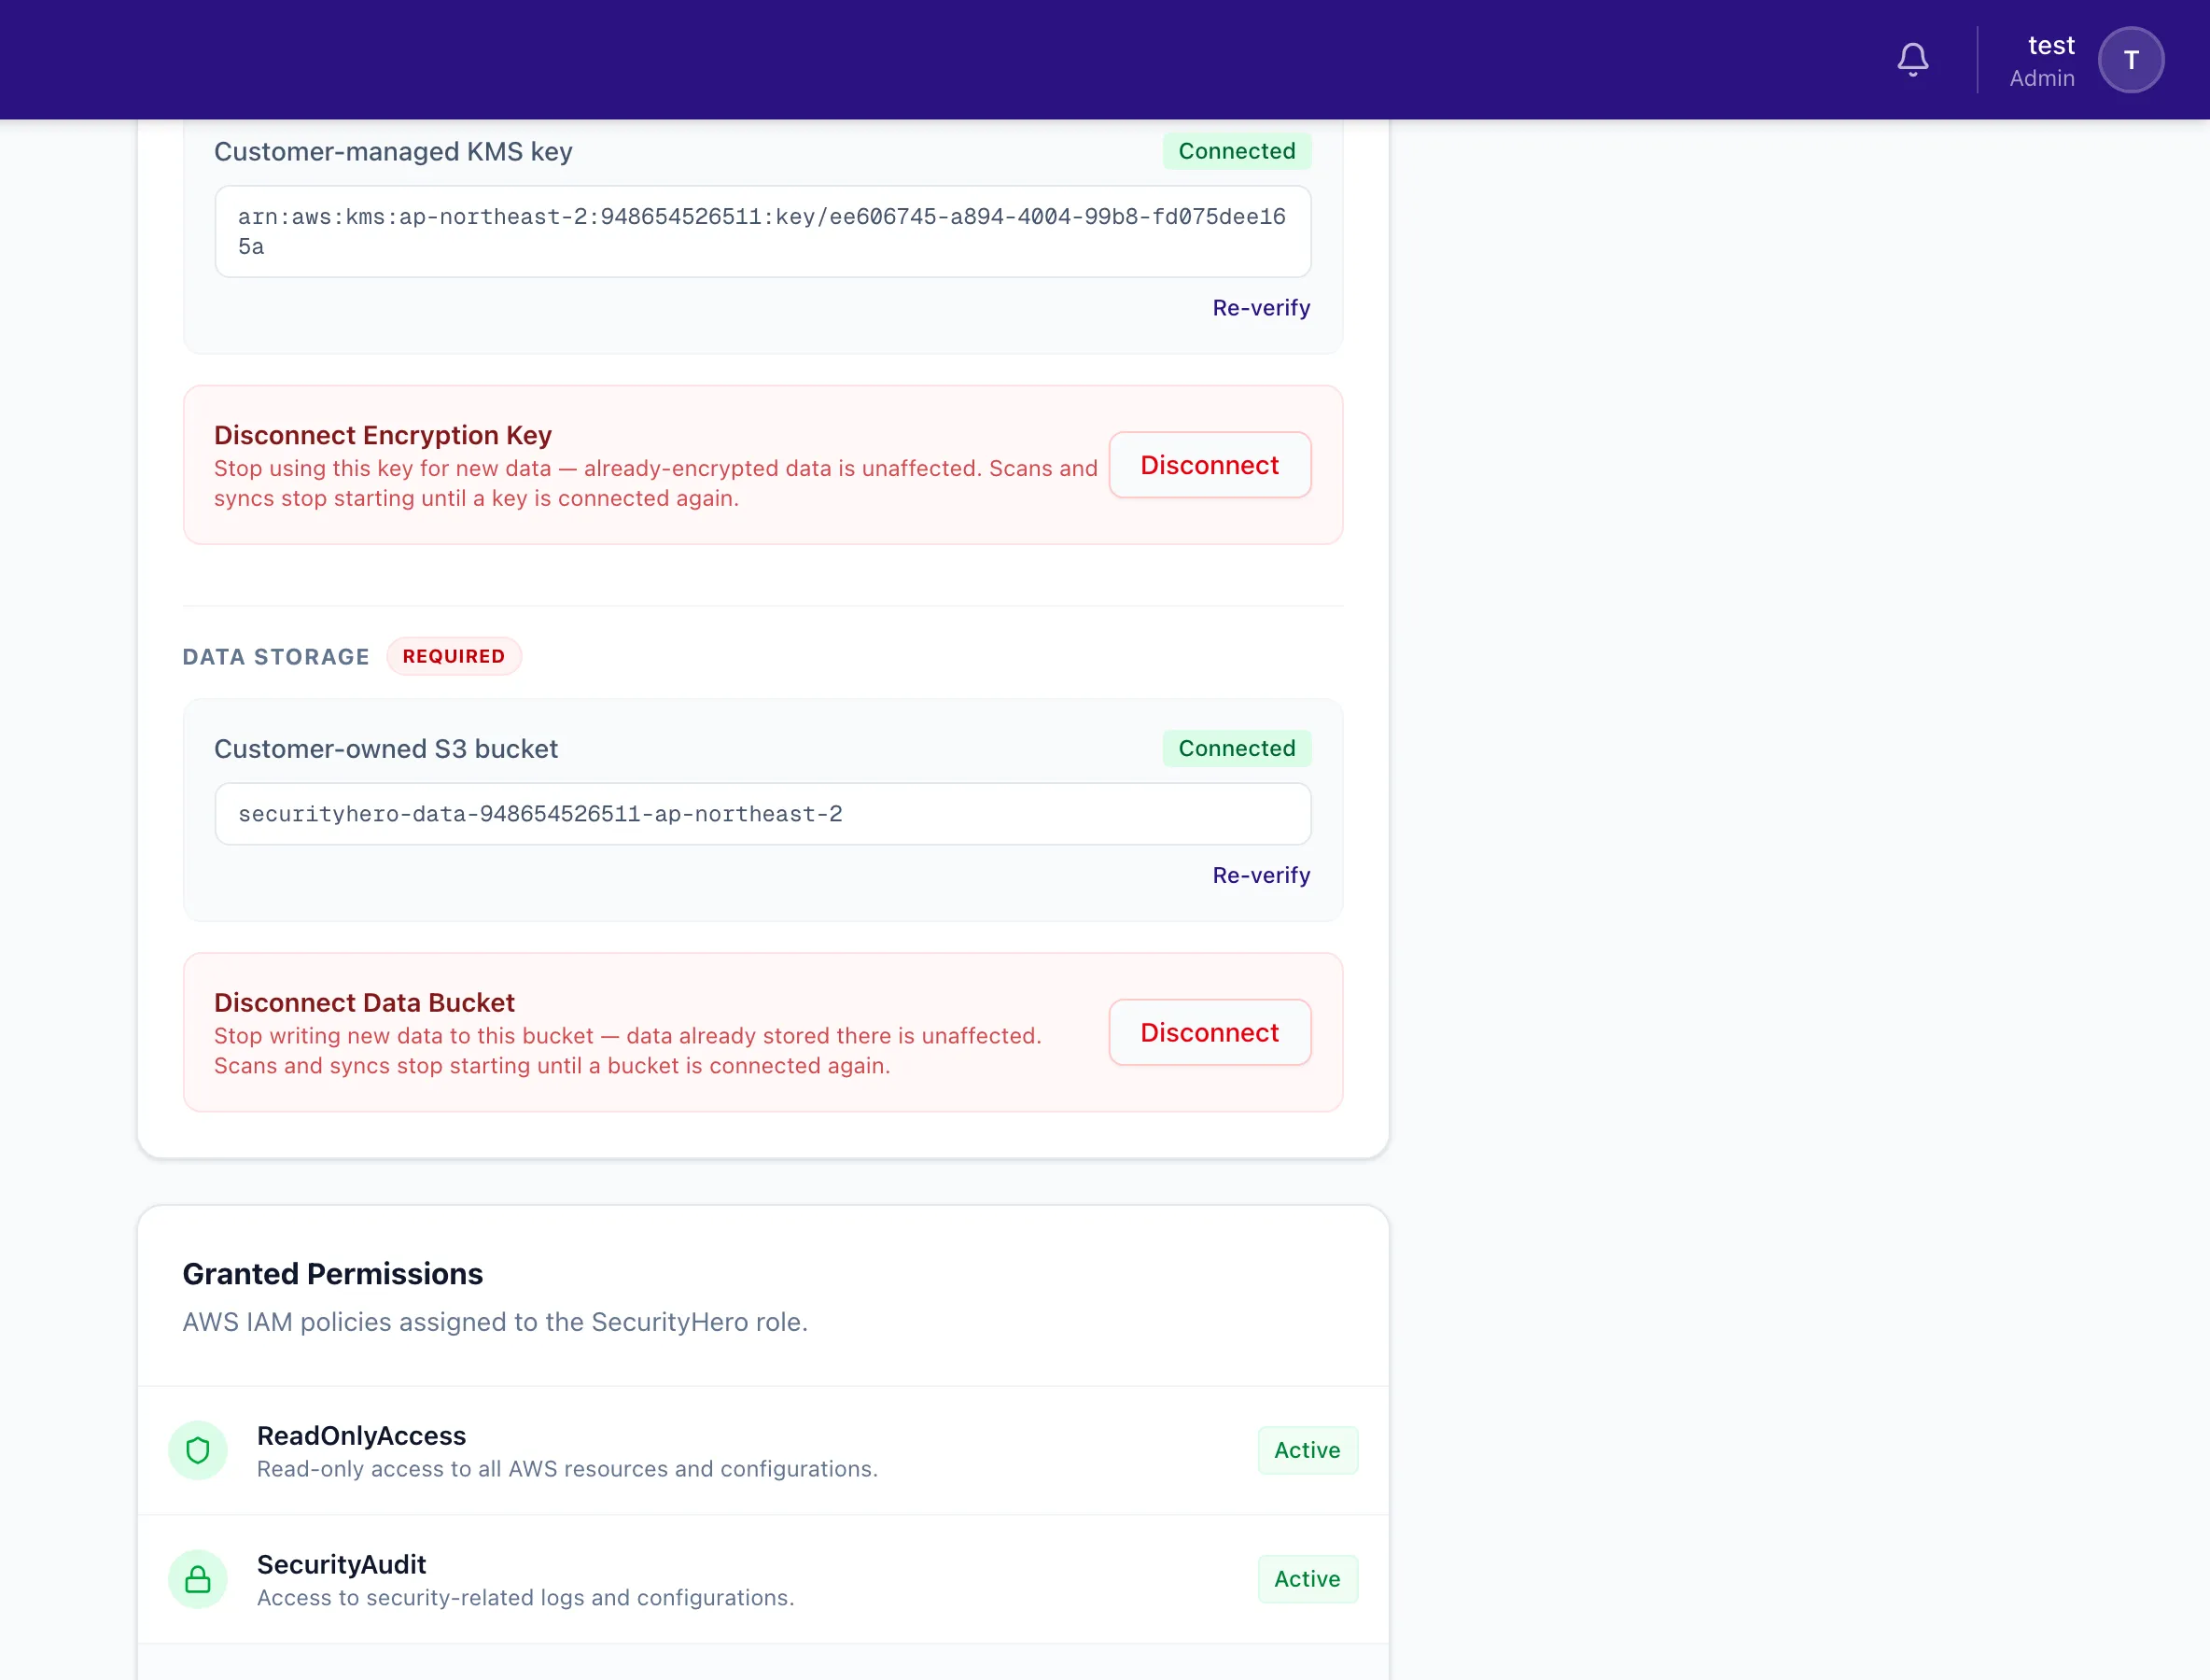
- Check whether each section is connected from its status badge (
Connected/Not set up). - After connecting, the key ARN, bucket name and region are shown, and you can verify again with the Re-verify link.
- Neither feature affects the existing role connection or how asset scans behave.
6. Frequently asked questions
- What happens if I do not connect them? Raw data is kept securely in storage managed by the service, and every feature works normally.
- Do I share AWS credentials? No. Like the AWS connection, this is based on CloudFormation and no access keys are shared.
- Do I need to redeploy the existing connection? No. Each feature only creates one additional stack; the existing IAM Role does not need to be redeployed.